Vulnerabilities
EPSS Score Mechanics: How Probability Drives Patch Prioritisation
The Exploit Prediction Scoring System predicts the likelihood of real-world exploitation, allowing teams to ignore high-CVE scores that rarely face active attacks.
Everything Packet Tribune has reported about vulnerability management: 7 stories, newest first. Part of our Vulnerabilities coverage.
The Exploit Prediction Scoring System predicts the likelihood of real-world exploitation, allowing teams to ignore high-CVE scores that rarely face active attacks.
Modern frameworks often ignore CSRF because they assume anti-forgery tokens are automatic, leaving state-changing endpoints vulnerable to silent exploitation.
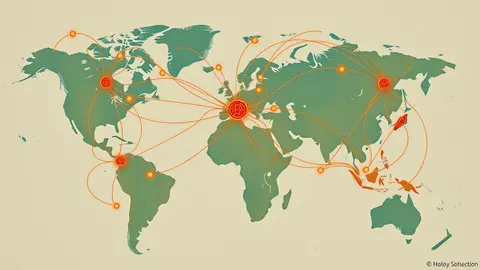
The global system relies on local coordinators who assign IDs based on product scope, not severity, creating a fragmented but scalable identification network.
Emergency patching bypasses standard change controls to neutralise active threats, trading procedural safety for immediate risk reduction.
Treating all vulnerabilities equally wastes resources; ranking by exploitability and asset value reveals which flaws actually endanger your organisation.
Most teams treat temporary workarounds as permanent fixes, creating hidden technical debt that outlives the original vulnerability and increases long-term risk.
The company’s new opt-in service uses advanced models to generate security reports for critical software, marking a shift in automated vulnerability detection.