Tech News
Should I enable firmware TPM and what breaks when you do
Enabling a firmware-based trusted platform module shifts cryptographic keys from external silicon to shared memory, creating a hidden performance tax.
Everything Packet Tribune has reported about hardware security: 3 stories, newest first. Part of our Tech News coverage.
Enabling a firmware-based trusted platform module shifts cryptographic keys from external silicon to shared memory, creating a hidden performance tax.
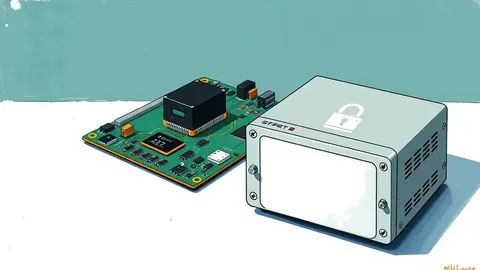
A hardware security module guards enterprise keys in network appliances while a trusted platform module anchors system boot integrity directly on the motherboard.
The hardware root of trust measures your system before booting, creating a cryptographic chain that halts startup if any component fails verification.