Vulnerabilities
Grav Login OAuth flaw exposes predictable credentials for unauthenticated access
Before version 1.4.3, the plugin sets unsalted MD5 passwords and deterministic usernames, enabling credential guessing attacks.
Before version 1.4.3, the plugin sets unsalted MD5 passwords and deterministic usernames, enabling credential guessing attacks.
A critical flaw in the Linksys E1700 allows remote attackers to exploit a stack-based buffer overflow, with public exploit code available.
The National Vulnerability Database lists a critical object injection flaw in Rosalinda versions up to 1.2.4, exposing sites to potential compromise.
Unpatched flaws in TOZED X300 firmware allow remote attackers to execute OS commands via the IPPingDiagnostics component.
Attackers can execute arbitrary OS commands via OpenSpug’s file transfer endpoint, with no patch confirmed by the vendor for affected releases.
A CVSS 9.8 vulnerability in the miniOrange OTP verification plugin allows attackers to escalate privileges on affected WordPress sites.
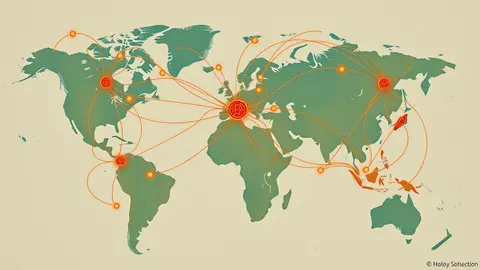
The global system relies on local coordinators who assign IDs based on product scope, not severity, creating a fragmented but scalable identification network.
Isolating the compromised device before rebooting prevents the attacker from wiping forensic evidence and re-establishing control over your network traffic.
Most API flaws stem from poor access controls rather than complex code errors, leaving user data exposed through misconfigured digital doors.
Updating dependencies is not merely a repair task; it is a continuous negotiation between software stability and the shrinking window of exploitability.
Emergency patching bypasses standard change controls to neutralise active threats, trading procedural safety for immediate risk reduction.
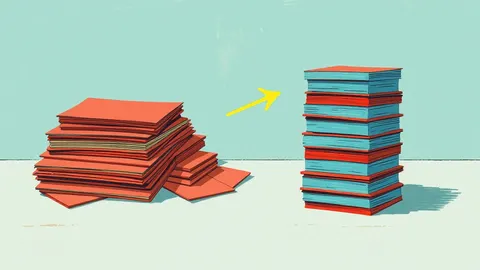
Treating all vulnerabilities equally wastes resources; ranking by exploitability and asset value reveals which flaws actually endanger your organisation.
Default login pages often sit on standard ports, making them easy targets for automated scans that ignore your main website traffic entirely.
Most teams treat temporary workarounds as permanent fixes, creating hidden technical debt that outlives the original vulnerability and increases long-term risk.
NoSQL injection bypasses traditional SQL filters, allowing attackers to extract data through logical operators that standard scanners often miss entirely.
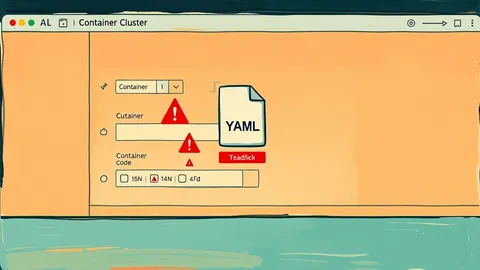
A high-severity flaw in Apache Camel Karavan allows authenticated users to deploy arbitrary Kubernetes resources, including privileged pods, via unvalidated YAML files.
A critical vulnerability in PraisonAI Agents allows LLM-generated code to access all environment variables, bypassing intended sandbox protections.
A missed middleware wrapper in Nginx UI allows attackers with valid JWTs to restart clusters and manage nodes without second-factor authentication.
The company’s new opt-in service uses advanced models to generate security reports for critical software, marking a shift in automated vulnerability detection.
IBM warns that improper authentication in Security Verify Access allows remote attackers to bypass security restrictions without a confirmed patch.
A CVSS 9.5 vulnerability in NetScaler ADC and Gateway allows remote code execution or denial-of-service when SAML is configured, affecting multiple versions.
Unauthenticated attackers can exploit a path traversal flaw in IBM Guardium v12.0-12.2 to execute arbitrary code, posing severe risk.