Vulnerabilities
What is security debt: the hidden costs of delayed fixes
Unresolved security shortcuts compound over time, creating a technical burden that eventually outweighs the initial speed gained by deferring proper controls.
Unresolved security shortcuts compound over time, creating a technical burden that eventually outweighs the initial speed gained by deferring proper controls.
Transport encryption protects data in motion but leaves stored messages vulnerable, creating a false sense of total security for untrained administrators.
OAuth tokens are ephemeral access passes that expire, while API keys are static identities that persist until manually revoked, creating distinct risk profiles for your infrastructure.
Layer 7 load balancers rewrite application data to mask backend vulnerabilities, creating a hidden attack surface that traditional perimeter devices cannot see.
Most container escapes bypass application-level security by exploiting the shared kernel, making host-level isolation the primary defence against lateral movement.
RSA encryption relies on the mathematical difficulty of factoring large prime numbers, creating a system where anyone can lock data but only the key holder can unlock it.
Digital signatures gain legal standing through cryptographic proof of identity and integrity, not merely through the visual appearance of a signed document.
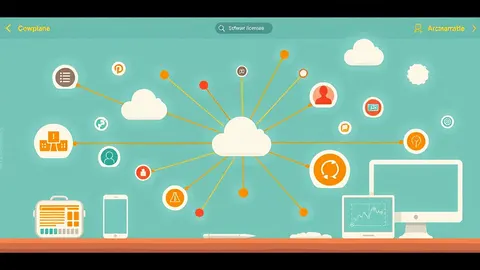
Most organisations lose track of software licences and shadow IT because their inventory methods ignore the dynamic nature of cloud services and temporary endpoints.
Operational technology failures often precede network alerts, meaning physical symptoms reveal intrusion before digital sensors trigger alarms.
Blocking outbound calls removes more risk from gift card fraud than training staff to recognise social engineering scripts.
AI data centers diverge from traditional facilities by prioritising high-density compute clusters and specialised cooling over standard server virtualisation practices.
Automated updates often break business logic, so you must isolate plugin changes in staging environments to prevent silent data corruption during security patches.
A mobile device management system enforces policy at the operating system level, preventing data loss even when users ignore security warnings or lose their phones.
Scareware bypasses technical defences by hijacking browser contexts to simulate operating system alerts, forcing immediate action before users can verify the threat.
Multi-factor authentication stops credential theft but fails if the attacker steals the second factor through session hijacking or SIM swapping attacks.
Botnets bypass perimeter defences by using your own devices as launchpads, making internal network segmentation the only effective barrier against lateral movement.
Doxxing shifts from harassment to criminal liability when it enables physical harm or facilitates further unauthorized access to restricted systems.
Most breaches occur because legacy access controls fail to map correctly to cloud identity models, leaving migrated assets exposed.
The shell translates human commands for the kernel, creating a security boundary that fails when privilege escalation bypasses the interface.
Code signing prevents tampering but does not verify that the signed code is safe or free from vulnerabilities.
AES relies on substitution-permutation networks rather than simple key swapping, making it resistant to most linear cryptanalysis methods used against older ciphers.
Callback verification blocks social engineering by forcing callers to prove identity through a separate channel, yet it fails against advanced impersonation.
Most data breaches stem from misconfigured systems rather than sophisticated hacking, meaning administrative discipline often matters more than advanced defensive tools.
Endpoint protection does not just block threats; it actively monitors system behaviour to stop attacks that bypass traditional signature matching.